Ransomware recovery of devices
Endpoint privilege management for advanced ransomware and threat protection.
Ransomware is a growing threat to organizations
In 2023 ransomware attackers extorted more than 1.1 billion dollars from organizations around the world. The total cost in lost productivity and remediation was much higher. By reducing the number of end users with administrative privileges it is estimated that 92% of malware and ransomware attacks can be prevented.
Overview
Microsoft recently released Microsoft Intune Endpoint Privilege Management which can elevate permissions when necessary.
However, removing administrative privileges is extremely challenging in an enterprise due to the lack of visibility into where and how administrative privileges are being used.
Threat vector identification
Administrators often struggle to identify important information:
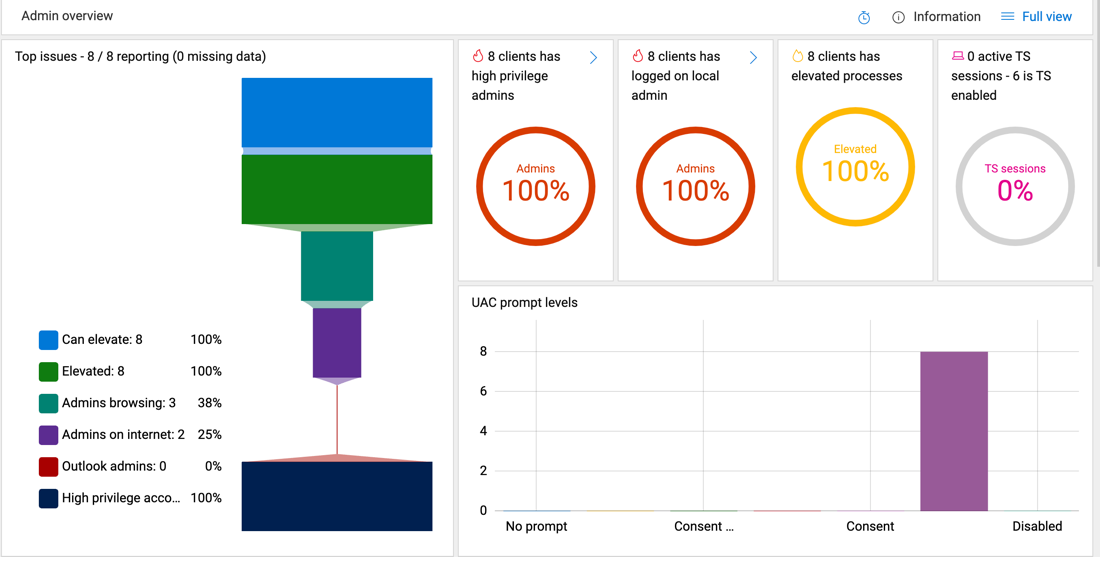
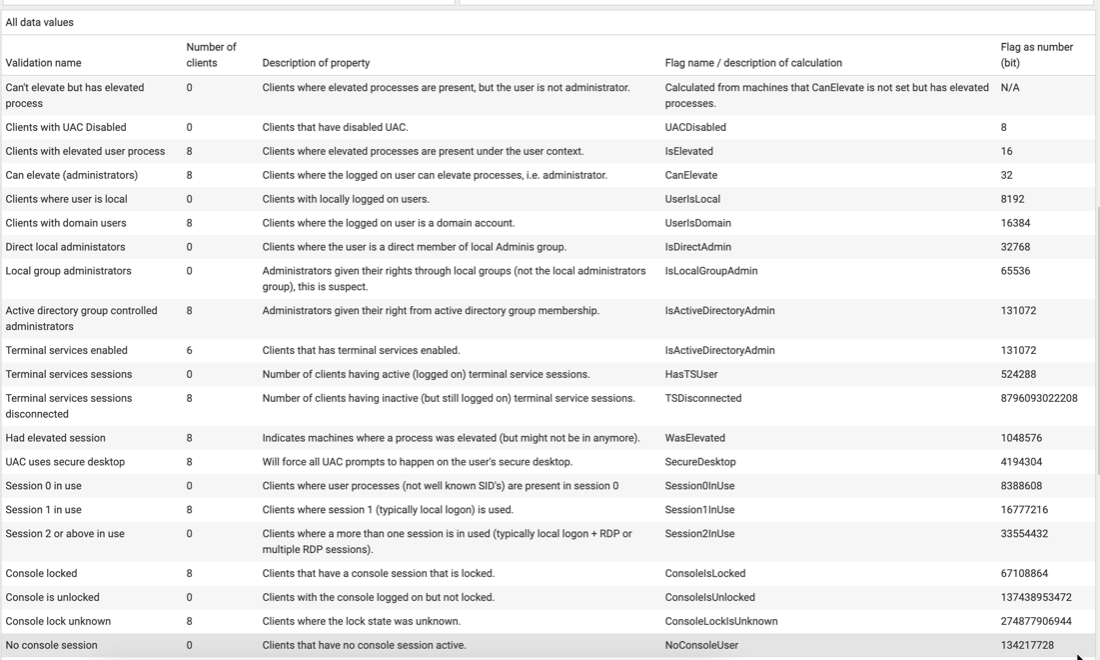
- How many endpoints have users logging on with administrative permissions?
- How many endpoints are running elevated processes?
- Are domain administrators logging on to endpoints?
- Is User Access Control configured properly across the enterprise?
Typical case
In an ideal world, IT departments would deploy all their endpoints at the same time, with common operating system versions. Devices would be fully patched and run the same software and drivers. Computers would operate in identically configured network environments with continuous Internet connectivity and IT managers would easily track updates and admin permissions.
The reality is much messier. Personnel come and go, and they work in multiple locations and time zones. Users need different role-specific software installed and permissions opened. Depending on the nature of their work they can have uneven and unpredictable requirements. Even the most diligent IT support staff may overlook a potential threat vector when managing hundreds or thousands of variably configured endpoints.

The challenge
What IT departments need is a readily accessible and efficient method to quickly check all enterprise endpoints for elevated permissions. Equipped with critical and timely information, managers can review privilege settings, identify active administrative processes, and remediate potential security threats.